One firm for every side of the deal
A deal has two sides, and both need the same thing: a straight answer about code neither of them wrote. We take the work from either side, the team shipping it or the people deciding whether to trust it, and we say plainly which one is paying.
Nobody should have to take a crypto claim on faith
Almost everything that goes wrong on-chain was knowable in advance. The code was public. The permissions were readable. The licence was checkable. Someone only had to look, and be paid by the person who needed the truth rather than the person selling it.
That is the whole of what we do. We look, we write down what we found, and we put our name on it. When a review is clean we say so plainly, and when it is not we say that too, to whoever is paying for the answer.
On-chain systems do not get a second attempt. Once a contract holds funds, the cost of a missed line is counted in other people's money, so we would rather be the ones who found it first.
Four questions, start to finish
- Check someone else's product
Commissioned by you, not by the project being assessed. Independent because of who is paying, not because of who is promising.
- Investor due diligence
- Partnership and integration analysis
- Neutral transaction verification
- Secure your own
Before launch, while fixing anything is still cheap.
- Web3 and protocol audit
- Penetration testing
- Tokenomics and yield review
- Deployment verification
- Formal verification
- Meet compliance requirements
What regulators, exchanges and users need to see.
- Compliance and business logic audit
- Proof of reserves
- Keep it safe in production
After launch, when the code is live and holding funds.
- Security advisory retainer
- Bug bounty triage
- Monitoring and incident retainer
- Build, harden and maintain
The standard every engagement meets
Secure at the code layer and sound at the architecture layer, every time. Where the engagement covers compliance, cleared for the markets it serves as well.
Our own tooling sweeps for known patterns. The judgment on every finding is human. No juniors, no shortcuts.
We think like someone trying to rob you, not like a checklist: rigging prices, jumping the queue on trades, buying enough votes to change the rules.
Findings apply to the scope and the commit the report names. We say what we did not look at, not only what we did.
Our name is on every attestation we issue. If we sign it, we stand behind it.
How we handle what you send us
Every line here is written into our Privacy Policy or Terms. If we break one, you have it in writing.
Signed before anything moves
A non-disclosure agreement is in place before code changes hands, on your paper or ours. Access is limited to the auditors on your engagement, on a need-to-know basis.
We never ask for keys
Not private keys, not seed phrases, not production credentials, and we will not accept them if offered. Anything we need to reproduce runs on a fork or a testnet. If someone claiming to be us asks you for a key, it is not us.
Nothing starts without authorisation
Written confirmation that you own the targets, or are entitled to have them tested, including anything hosted by a third party. We do not start without it.
Your code never trains a model
We do not use your code to train models, and we do not feed it to third-party AI services. It stays inside the engagement and nowhere else.
Hardware keys, encrypted devices
Multi-factor authentication and hardware keys on every account that can reach client material. Full-disk encryption on company devices, and no client code on personal machines.
Access ends when the work does
Access is granted per engagement and revoked when it closes. Source code and repository copies are deleted within 90 days of final delivery, unless you ask us in writing to keep them for a re-audit.
Nothing published without your word
A public attestation states only what you have approved us to state. Findings are never shared with other clients: generic lessons may inform our methodology, your specifics never leave the engagement.
Paid by you, not by who we assess
On due diligence and partnership work the buyer commissions us, never the project under assessment. The fee is fixed before we start and does not change with what we conclude.
This site collects nothing
No cookies, no analytics, no trackers, no database. The contact form sends one email to our own mailbox and your address is used to reply to you, nothing else.
These cover how we run the firm and handle your material. None of them is a statement about the code we review: that is what the report says, and only for the scope and commit it names.
The people who lead the work
The seats that run the firm and its engagements. Specialists join per engagement.
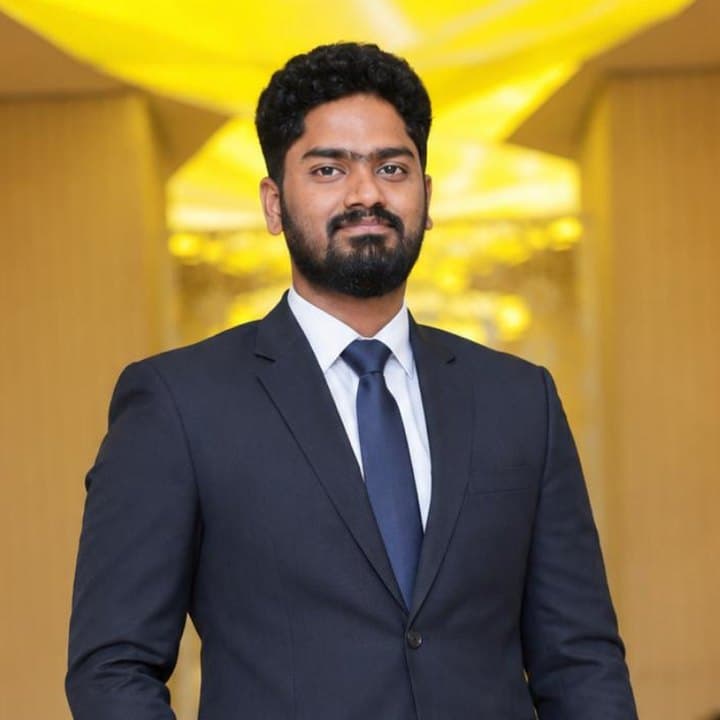
Prabhat Babu
Founder, Head of Internal Security & Lead Auditor
India
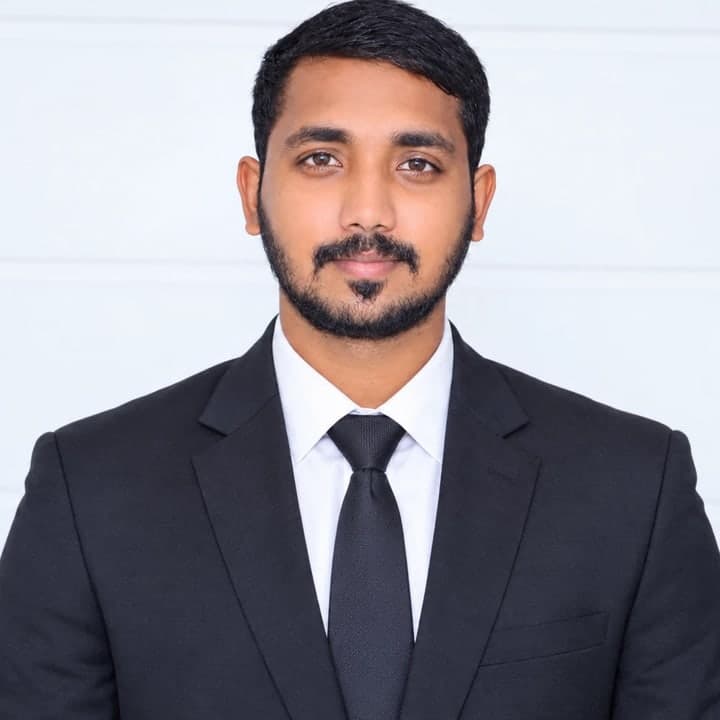
Harikesh
Operations Lead
India
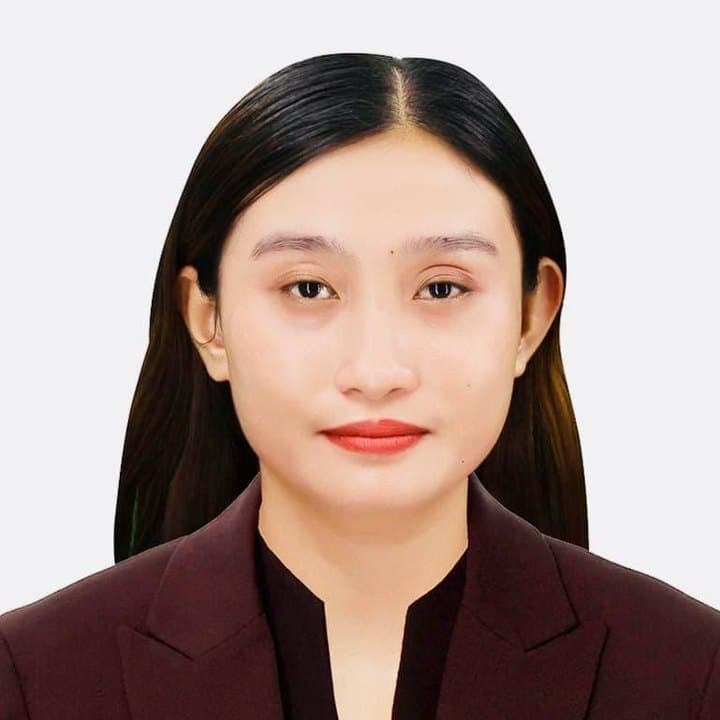
Shekinah Glory Rabara
Marketing Head
Philippines
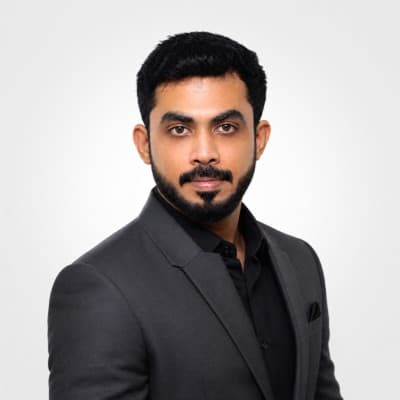
Anup Kumar
Business Development Advisor
India
Rishi Narayanan
Strategic Advisor, BD & Compliance
USA
Bennet Enstein
Human Resources Consultant
India
Mario Butler
Advisor
USA